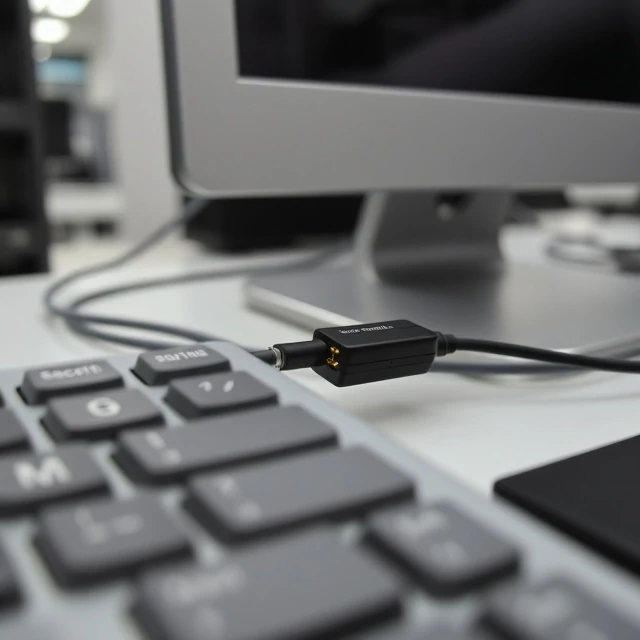
A keylogger records keystrokes. Software keyloggers run as hidden processes on a compromised machine. They capture everything typed: passwords, messages, credit card numbers, and search queries. Hardware keyloggers plug in between the keyboard and the computer. They look like a small adapter and store data internally or transmit it wirelessly. Both types are hard to detect. Software keyloggers hide in legitimate-looking processes. Hardware keyloggers are invisible to antivirus software.
Keyloggers are a staple of credential theft. Attackers use them to harvest logins for banking, email, and corporate systems. Some are deployed by malware. Others are installed by someone with physical access, like a jealous partner or a malicious insider. Detection is difficult. Behavioral analysis might catch a process that reads keystrokes and sends data outbound. Antivirus tools catch known keylogger signatures. Neither is reliable against custom malware. Defense is layered. Use multifactor authentication so a stolen password is not enough. Use a password manager that fills credentials without typing. Check for physical devices on your keyboard cable. Keep software patched. On shared computers, assume someone may be watching. A keylogger turns your keyboard into a spy.
Keylogger types
- Software — hidden process on the operating system
- Hardware — physical device inline with the keyboard
- Kernel-level — rootkit that hides deep in the OS
- Acoustic — analyzes keyboard sounds to infer keystrokes
Multifactor authentication does not stop a keylogger from stealing your password. It stops the attacker from using it.
Comments
No comments yet. Be the first to share a thought.
Leave a comment